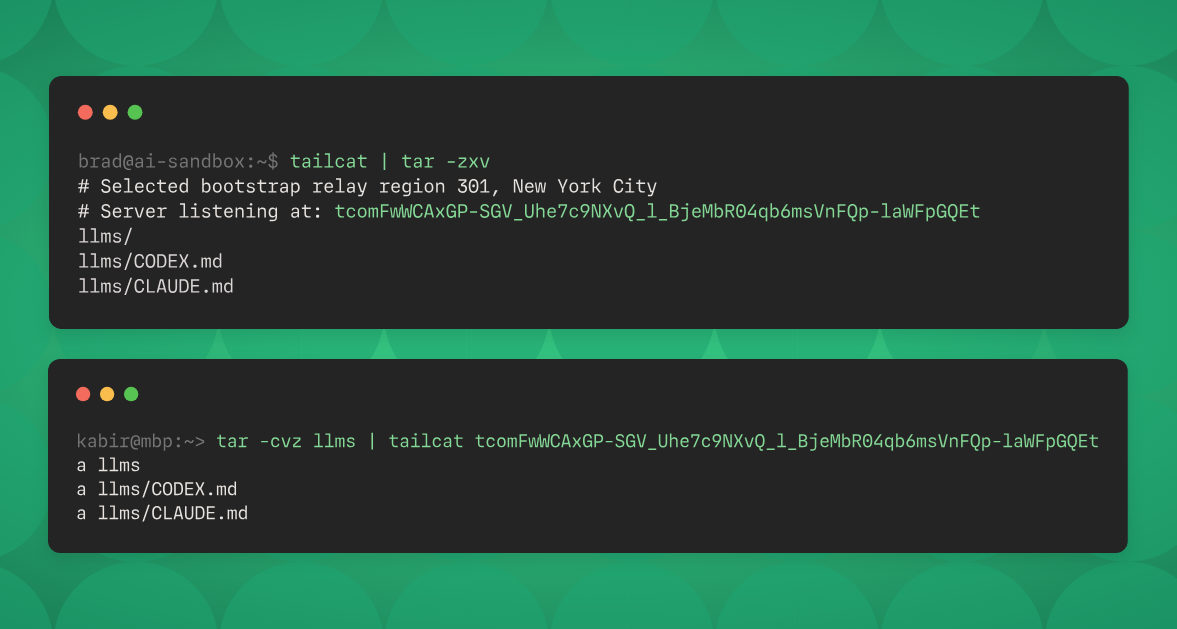
Tailscale ‚tailcat‘– is both an open-source Go package and a CLI tool using that package it lets you run a server side listener and a client to connect to that server moving bidirectional bytes back and forth
root@pve-tailcat-01:~#
root@pve-tailcat-01:~# ./tailcat >> remote_logs.txt # Selected bootstrap relay region 303, Frankfurt # 🐈 Server listening with new address: <tcp…QEv>
root@pve-tailcat-0a:~#
root@pve-tailcat-02:~#
root@pve-tailcat-02:~# echo „Server-Neustart durchgeführt um $(date)“ | ./tailcat <tcp…QEv>
root@pve-tailcat-02:~#
root@pve-tailcat-01:~#
root@pve-tailcat-01:~# cat remote_logs.txt Server-Neustart durchgeführt um Tue Oct 13 09:36:34 UTC 2026
root@pve-tailcat-01:~#
root@pve-tailcat-02:~# echo „Server-Neustart durchgeführt um $(date)“ | ./tailcat <tcp…QEv>
root@pve-tailcat-01:~#
root@pve-tailcat-02:~#
root@pve-tailcat-01:~# cat remote_logs.txt Server-Neustart durchgeführt um Tue Oct 13 09:36:34 UTC 2026 Server-Neustart durchgeführt um Tue Oct 13 09:58:13 UTC 2026
root@pve-tailcat-01:~#
root@pve-tailcat-01:~#
root@pve-tailcat-01:~# ./tailcat genkey –key=pve-tailcat-01 # wrote file to /root/.config/tailcat/keys/pve-tailcat-01.private.json <tcp…pIA>
congstar Homespot & Go – congstar defaults to the Telekom IPv6 network if a website or app does not fully support IPv6 the provider’s NAT64 gateway must translate it if this gateway glitches DNS succeeds but the page won’t open
Fix: Change your APN profile from internet.v6.telekom to the legacy fallback internet.telekom (or internet.congstar) and ensure the APN protocol is set to IPv4/IPv6 (Dual Stack) instead of IPv6-only
Es geht um den Fernzugriff der es ermöglicht auch von außerhalb des eigenen Zuhauses über das Internet auf den Router zuzugreifen diese Verbindung kann jedoch ein Einfallstor für Angreifer darstellen weshalb das Bundesamt für Sicherheit in der Informationstechnik (BSI) zur Vorsicht rät
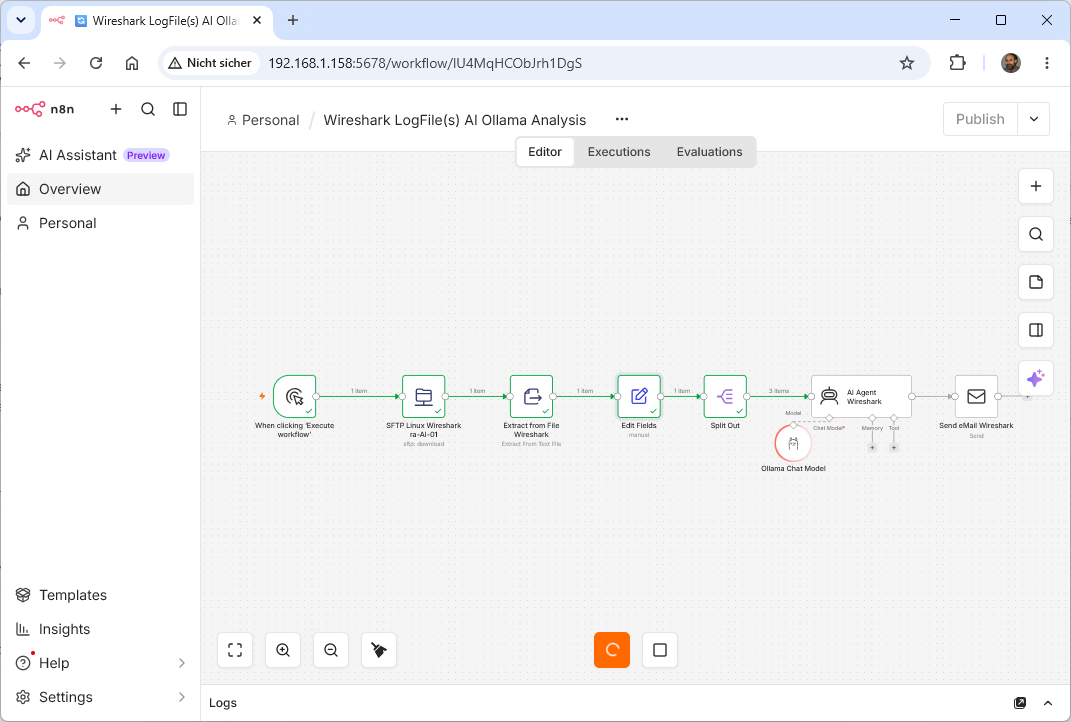
At first LLMs cannot open raw „*.pcap“ files directly you must first convert the data into a readable format and do not try to upload millions of rows use Wireshark display filters (like http ip.addr == 192.168.1.1 or tcp.flags.syn == 1) to isolate the suspicious or relevant traffic
FRITZ!Box Packet Sniffer – capture network traffic directly on the FRITZ!Box and record it live using Wireshark
Example of a Wireshark Display Filter for an IP client in a home lab
Sortiere nach technischem Risiko und Relevanz, nicht einfach nach Anzahl der Pakete.
9. Wireshark Display Filters
Gib für jedes relevante Finding passende Wireshark Display Filters an.
Beispiele:
tcp.analysis.retransmission
tcp.analysis.duplicate_ack
tcp.flags.syn == 1
tcp.flags.reset == 1
dns
http
tls
arp
icmp
Erstelle zusätzlich spezifische Filter für die tatsächlich gefundenen IPs, Ports, Domains oder Protokolle.
10. Final Traffic-Light Dashboard
Schließe den Bericht mit einem kompakten Dashboard ab:
Category Status
Network Health 🟢/🟡/🔴
Security 🟢/🟡/🔴
Performance 🟢/🟡/🔴
Protocol Health 🟢/🟡/🔴
Configuration 🟢/🟡/🔴
Overall Assessment 🟢/🟡/🔴
Ampel-Regeln
🟢 GREEN: Kein relevanter Hinweis auf ein Problem.
🟡 YELLOW: Auffälligkeit vorhanden, aber nicht ausreichend für eine kritische Bewertung. Weitere Untersuchung empfohlen.
🔴 RED: Starke Evidenz für ein relevantes Security-, Performance- oder Netzwerkproblem.
Wichtig
Erfinde keine Daten, IPs, Domains oder Ereignisse.
Verwende ausschließlich Informationen, die aus der PCAP-Datei oder eindeutig daraus abgeleiteten Statistiken stammen.
Gib bei jeder kritischen Aussage die zugrunde liegende Evidence an.
Trenne Fakten von Interpretation und Hypothesen.
Wenn die PCAP keine ausreichenden Informationen für eine Aussage enthält, schreibe ausdrücklich „nicht bestimmbar anhand der vorliegenden PCAP“.
Bewerte nicht nur einzelne Pakete, sondern auch Kommunikationsmuster und zeitliche Zusammenhänge.
Hebe besonders relevante Findings hervor und vermeide eine reine Auflistung unkritischer Pakete.
Ziel: Ein Bericht, der sowohl für einen Network Engineer als auch für einen Security Analyst verständlich ist und anhand der Traffic-Light-Matrix sofort erkennen lässt, wo Handlungsbedarf besteht.
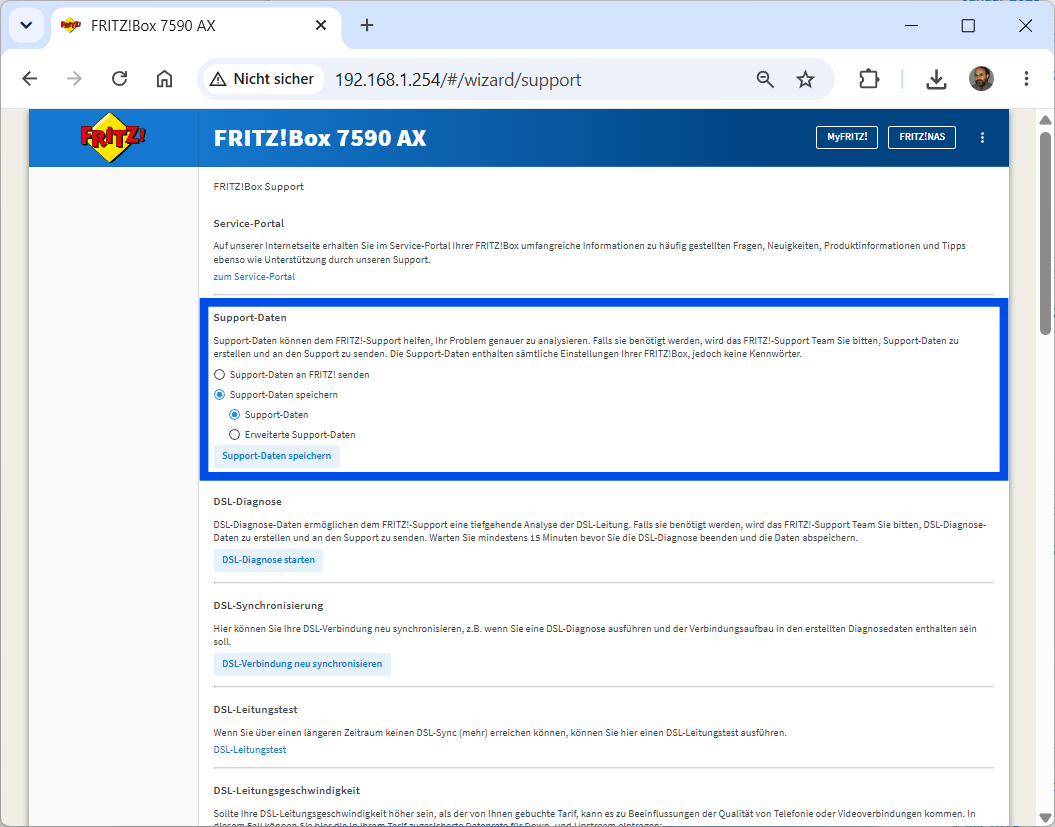
Wenn man tiefere technische Details sucht können die Support Daten der FRITZ!Box ausgelesen werden diese enthalten interne Konfigurationen (wie z.B.: Teile der smb.conf) und Kernel Logbucheinträge
 Es geht um den Fernzugriff der es ermöglicht auch von außerhalb des eigenen Zuhauses über das Internet auf den Router zuzugreifen diese Verbindung kann jedoch ein Einfallstor für Angreifer darstellen weshalb das
 FRITZ!Box Packet Sniffer – capture network traffic directly on the FRITZ!Box and record it live using Wireshark

 Wenn man tiefere technische Details sucht können die Support Daten der FRITZ!Box ausgelesen werden diese enthalten interne Konfigurationen (wie z.B.: Teile der smb.conf) und Kernel Logbucheinträge